Enterprises Still Can't Govern Their AI Agents. The EU's Next Deadline Is 2 December.
AI agent governance means knowing which agents run, under which identity, and what each one did. Under the EU AI Act, agents that talk to people must disclose they are AI from 2 August 2026, while Annex III high-risk duties start 2 December 2027. In a 285-person CSA survey, 84% doubted they would pass an agent audit.
The short version
The EU moved its high-risk AI rules to December 2027, but Article 50 transparency has applied since 2 August 2026 and marking for older generative systems is due 2 December. Two CSA surveys show only 21% of organisations keep a real-time agent registry, so most cannot yet list the agents they would have to govern.
Want this decided for your own case? Find your tools with Smart Match, starting from this guide's question.
On 31 March 2026, OpenAI closed a $122 billion funding round, and a packaging mistake pushed the source code of Anthropic's coding agent onto the public npm registry. We first wrote this piece on 4 August. Several numbers we printed then were wrong, and the deadline that matters next is 2 December 2026.
That is the date the EU's AI-content marking duty reaches generative systems that were already on the market before August. The high-risk regime most compliance teams filed away has moved to December 2027, which makes it easy to assume nothing is due this year. For a security or platform lead running agents in production, the next six weeks are the near-term exposure, and the identity gap underneath them has not closed.
What changed since our 4 August version
We re-checked every claim in the original against its primary source on 21 October 2026. Eight did not survive in the form we printed them.
| What we said in August | What the source says | Source |
|---|---|---|
| Article 50 "lands next week" | Applies since 2 August 2026 | European Commission |
| The Council "finalized" the delay on 29 June | In force 27 July, after publication on 24 July | Official Journal, via Lewis Silkin |
| "Nearly 70%" run agents in production | 85% in a 228-person CSA survey | CSA, 24 March |
| 82% lack identity confidence | Not in either CSA release; cut | None found |
| 23% have a formal agent identity strategy | Not in either CSA release; cut | None found |
| 44% "still authenticate" with static keys | 44% use or plan to use static API keys | CSA, 5 February |
| Leak "forked more than 41,500 times" | "Tens of thousands" of forks | Zscaler ThreatLabz |
| Iran's threat was "set to expire" 1 April | Attacks were set to begin 1 April | CNBC |
Two of those errors came from one mistake. The original attributed six survey figures to a single Cloud Security Alliance release, when they came from two different CSA surveys with different sponsors, samples and dates. Four of the six are real. Two, the 82% and the 23%, appear in neither release, so they are gone.
The attribution of the Iranian industrial attacks also changed. The original named the CyberAv3ngers group. The US joint advisory does not: it blames an unnamed Iranian-affiliated group and cites CyberAv3ngers only as a 2023 precedent. The section on that campaign below follows the advisory's wording.
The EU calendar now has four dates, and one is six weeks away
The Digital Omnibus on AI was published in the Official Journal on 24 July 2026 and entered into force on 27 July, according to a Lewis Silkin briefing written that day. EU lawmakers had reached the political deal on 7 May, Travers Smith reported. The result is a staggered calendar rather than one cliff edge. The law itself is Regulation (EU) 2026/1744, dated 8 July 2026.
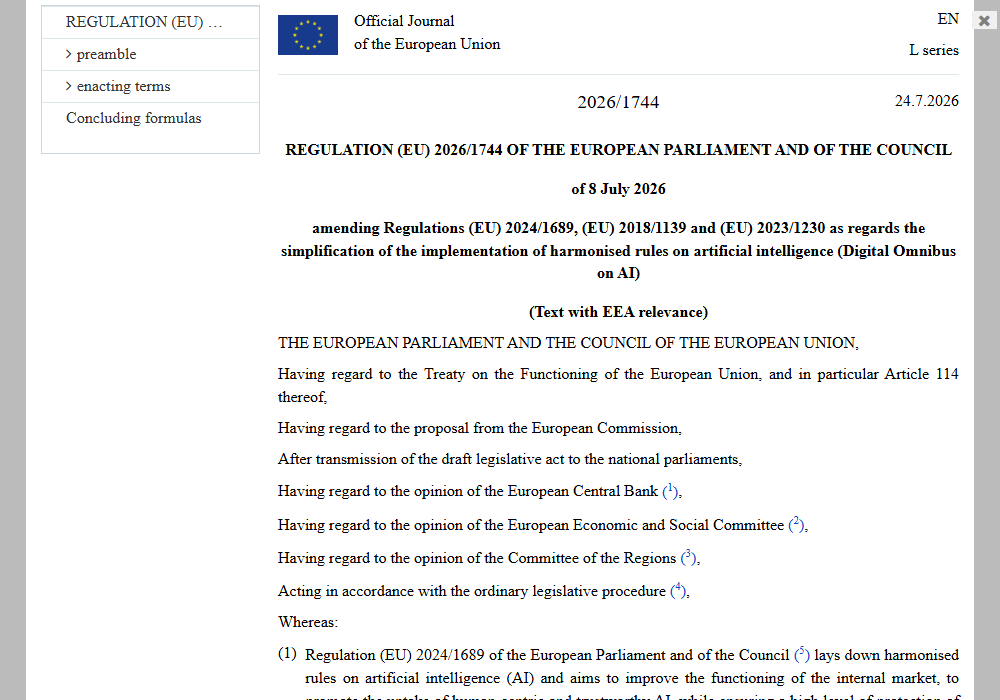 First page of the Omnibus regulation on EUR-Lex, the proof that the delay is law, captured 21 Oct 2026.
| Date | What applies | Who carries it |
|---|---|---|
| 2 August 2026 | Article 50 transparency, including telling people they face AI | Providers and deployers |
| 2 December 2026 | Machine-readable marking for systems launched before 2 August | Providers of generative systems |
| 2 December 2027 | Annex III high-risk rules: hiring, credit, education, infrastructure | High-risk providers and deployers |
| 2 August 2028 | Annex I rules for AI inside regulated products | Product manufacturers |
The Annex III move is a 16-month postponement, and the Annex I move is 12 months, according to Travers Smith. The same deal cut the marking grace period to three months from the six first proposed. Content generated before 2 August does not need a label after the fact, the Commission's Article 50 FAQ says, though it encourages deployers to add one where they can.
So the honest summary is narrower than "the EU delayed the AI Act". It delayed the expensive part. The cheap, visible part has applied for eleven weeks.
Who this affects: any team whose agent talks to the public
The Commission's FAQ is unusually direct about agents. Providers must design systems that interact with people, which it lists as "chatbots, AI agents, and avatars", so that people are told they are dealing with AI. Providers must also mark generative output with machine-readable signals that let it be detected as AI-made.
A provider outside the EU is still covered when its system's output is used in the EU. Deployers carry a separate set of duties:
- tell people when an emotion recognition or biometric categorisation system is used on them;
- label deepfakes;
- label AI-generated text published on matters of public interest without human review or editorial control.
If your team built a customer-facing agent on top of a model, you are probably its provider for these purposes, not merely a deployer. The directory of AI agents is a quick way to see how many shipped products now talk to the public in their own voice, and each of them sits under the first bullet of that FAQ.
The practical route to compliance is a voluntary code. The Commission published the final Code of Practice on Transparency of AI-generated Content on 10 June 2026, and the Commission and the AI Board have confirmed it as adequate, according to the Commission's code page. Signatories can rely on its measures to show compliance. Anyone who complies another way must prove adequacy to each market surveillance authority that asks.
Governance platforms such as Openlayer now map controls to the AI Act, and detection vendors such as Resemble AI sell the other side of the marking problem. Neither replaces the paperwork. They make it cheaper to produce.
Two CSA surveys, measured six months apart
The identity numbers deserve the most care, because they are the ones most often quoted without their sample. Both come from the Cloud Security Alliance, and both were commissioned and paid for by identity-security vendors.
| February 2026 release | March 2026 release | |
|---|---|---|
| Sponsor | Strata Identity | Aembit |
| Fielded | September to October 2025 | January 2026 |
| Respondents | 285 IT and security staff | 228 IT and security staff |
| Headline | 84% doubt they would pass an agent audit | 68% cannot tell agent from human activity |
From the Strata-sponsored survey, released on 5 February:
- 18% are "highly confident" their identity systems can manage agents; 29% are only slightly confident.
- 21% keep a real-time registry or inventory of their agents.
- 28% can reliably trace an agent's action to a human or system across all environments.
- 44% use or plan to use static API keys for agents, and 43% username and password pairs.
- 40% are raising identity and security budgets to cover agents.
From the Aembit-sponsored survey, released on 24 March:
- 85% use AI agents in production environments.
- 52% run agents under workload identities, 43% under shared service accounts, and 31% under human user identities.
- 74% say agents often get more access than they need.
- Only 9% name the identity team as the primary owner of agent access.
Read together, the two samples point the same way, and that is about as far as they go. Neither is a random sample of enterprises, and the sponsors profit from the problem being large. Still, a 21% registry rate is hard to argue up. You cannot govern an agent you cannot list.
Login-era identity was not built for agents
The mechanism behind those numbers is architectural. Directory systems like Microsoft's were designed around a person signing in, a session opening, and a human making judgement calls inside it. An agent has no session in that sense. It receives a credential, works through a plan it may change on every run, and stops.
That is why the 31% figure matters more than the headline. An agent running under a human's identity makes every action look like that person's. When something goes wrong, the audit log names the wrong actor, and the 28% traceability figure is the result.
Tool brokers concentrate the same risk. A connector such as Composio handles OAuth for hundreds of apps behind one endpoint, which is convenient precisely because one credential reaches many systems. Spending is next: AgentCard issues prepaid cards to agents and now requires identity verification for every card. For what that looks like once the money is live, see our test of agents handling real money. The open question is rarely capability. It is who answers for the transaction.
The Claude Code leak was a packaging error, which is the point
On 31 March, version 2.1.88 of Anthropic's npm package shipped with a 59.8 MB JavaScript source map, according to Zscaler's ThreatLabz team. The file held about 513,000 lines of unobfuscated TypeScript across 1,906 files. Security researcher Chaofan Shou flagged it publicly, and copies spread to GitHub, where they were forked tens of thousands of times.
Anthropic told CNBC it was "a release packaging issue caused by human error, not a security breach", and that no customer data or credentials were exposed. Zscaler traced the cause to the Bun runtime generating a full source map by default, with *.map files missing from the package's exclusion list. Model weights and user data were not in the file.
The same morning brought a second, unrelated problem. Malicious versions of the widely used axios library were published to npm between 00:21 and 03:29 UTC. Anyone who installed or updated Claude Code through npm in that window may have pulled a remote access trojan with it, The Hacker News reported, and the advice was to downgrade and rotate every secret. Soon after, fake "leaked Claude Code" repositories were distributing the Vidar infostealer and GhostSocks proxy malware, Zscaler found.
None of this needed an attacker to breach Anthropic. A build default, a missing ignore rule and a poisoned dependency did the work. Every coding agent your developers run, whether OpenAI's Codex, Gemini CLI or an editor such as Cursor, arrives through a release pipeline you do not control. Our comparison of Cursor and Claude Code covers the two most common picks. Whichever you choose, a poisoned install inherits the same access to the developer's machine.
Iran's PLC campaign shows what an unwatched access path costs
On 31 March, Iran's Revolutionary Guard named 18 companies as "legitimate targets", CNBC reported, including Nvidia, Apple, Microsoft and Google. It said attacks would begin at 8 p.m. Tehran time on 1 April. We found no public report tying a breach to that specific warning.
The industrial campaign is documented. Advisory AA26-097A, first published on 7 April and updated on 22 July, is signed by seven US agencies, including the FBI, CISA, the NSA and the Treasury. It says an Iranian-affiliated group has disrupted programmable logic controllers since at least March 2026, in local government, water and energy.
The July update widened the target list:
- Rockwell Automation CompactLogix and Micro850 controllers;
- Schneider Electric Modicon M340 controllers;
- Siemens S7-1200 controllers.
The actors used the vendors' own configuration software to copy project files out, then altered logic and manipulated what operators saw on their HMI and SCADA screens. In some cases the changes disabled shutdown and alarm logic, letting systems enter unsafe conditions. Some victims suffered operational disruption and financial loss.
These were not AI agents. The lesson carries over anyway: a device reachable from the internet, trusted tooling, and no one watching what changed. An agent with standing credentials and an API endpoint fits that description closely.
The case for waiting is real, and it is weaker than it looks
The strongest argument against urgency goes like this. Annex III, the part with conformity assessments and audit trails, is 13 months out. Article 50 asks mostly for disclosure and labels, which are cheap. The identity surveys are vendor-funded. On that reading, a sensible team finishes its 2026 roadmap and starts agent governance in the new year.
Three things break that plan. The marking deadline for existing generative systems is 2 December, not 2027. The two incidents above needed no regulation to cause damage, only a credential or an install path nobody was watching. And registries are slow to build: if 21% of organisations had one in late 2025, most will not have a complete one by the time Annex III arrives unless they start now.
What to do before 2 December
- List every agent you run, who owns it, and which credential it uses. Our guide to the three jobs of agent observability is a starting point for the logging side.
- For each one, decide whether you are its provider or its deployer under the AI Act. The duties differ.
- Make sure any agent that talks to the public tells people it is AI, inside the conversation itself.
- For generative systems launched before 2 August, ship machine-readable marking by 2 December, or sign the Code of Practice and follow its measures.
- Move agents off human and shared accounts onto their own identities, and replace static keys with scoped, short-lived credentials.
- Pin agent tooling versions and wait a cooling-off period before adopting a new npm release, as Zscaler advised after the leak.
- Take control systems and admin consoles off direct internet access, the first mitigation in the CISA advisory.
For the agent-facing layer, guardrail products such as Dynamo AI and HiddenLayer watch runtime behaviour, while code-scanning agents such as Codex Security and Vega look for flaws before release. The wider AI security tools directory lists the rest. If you are choosing between them for a specific stack, answer a few questions and get a shortlist matched to your use.
Teams that build their own agents should also read our roundup of AI agent builders, because the builder you pick decides where credentials live. The same applies to hosted options covered in our OpenAI Agents API pricing breakdown.
What would change this verdict
Three developments would. A large signatory list for the Code of Practice would make marking a solved commodity problem by December. A third CSA survey showing registry coverage well above 21% would weaken the case that identity is the bottleneck. And a disclosed incident in which an agent's own credential, not a human's, was the entry point would turn this from a governance argument into an insurance one.
The first marker to watch is 2 December itself. After that date, an EU market surveillance authority can ask a provider of an older generative system to show its marking, and "the high-risk rules moved to 2027" will not be an answer.
Frequently asked questions
Did the EU delay the AI Act rules that cover AI agents?
Partly. The Digital Omnibus on AI, in force since 27 July 2026, moved Annex III high-risk obligations to 2 December 2027 and Annex I product rules to 2 August 2028. Article 50 transparency, including telling people they are talking to an AI agent, was not delayed and has applied since 2 August 2026.
What is due on 2 December 2026 under Article 50?
Providers of generative AI systems placed on the market before 2 August 2026 must mark their output in a machine-readable, detectable way from that date. Systems launched on or after 2 August already had to comply. The Commission says content generated before 2 August does not need a retroactive label.
How many companies can actually track their AI agents?
Few, on the available evidence. In a Cloud Security Alliance survey of 285 IT and security staff, sponsored by Strata Identity and fielded in late 2025, 21% kept a real-time agent registry and 28% could trace agent actions to a human or system across all environments.
Was customer data exposed in the Claude Code source leak?
Anthropic said no customer data or credentials were exposed and called the 31 March incident a release packaging error. The bigger risk that morning was unrelated: malicious axios releases on npm, which anyone installing Claude Code through npm between 00:21 and 03:29 UTC may have pulled in.
Who is behind the 2026 attacks on industrial controllers?
Joint US advisory AA26-097A attributes them to an Iranian-affiliated group active since at least March 2026, and cites the IRGC-linked CyberAv3ngers only as a similar 2023 campaign. Targets include Rockwell Automation, Schneider Electric and Siemens controllers in water, energy and local government.
Covered in this guide
- AgentCard: Agentcard gives AI agents a way to pay online without seeing a card number, through a stored-card Vault or newly issued Issuing cards. It works with MCP clients, agent browsers and iMessage front ends.
- Anthropic: Anthropic is a Public Benefit Corporation started by 7 ex-OpenAI researchers. It builds the Claude model family and counts Amazon and Google among its largest backers.
- Codex Security: OpenAI's application security agent scans connected GitHub repositories, tests likely bugs in a sandbox, and drafts fixes for review as pull requests.
- Composio: Agents call one Composio endpoint to search, authorise and run tools across hundreds of apps; 11 meta-tools, OAuth handled for you.
- Cursor: Cursor is an AI code editor built on VS Code, widely adopted across large enterprise engineering teams, with Agent Mode, Tab completion, and Cloud Agents.
- Dynamo AI: Enterprise AI guardrail platform whose AgentWarden cut a tested MCP deployment's attack surface by 97% in under 5 minutes.
- Gemini CLI: Google's open-source coding agent for the terminal, now limited to enterprise Code Assist licenses after its June 2026 consumer shutdown.
- HiddenLayer: AI security platform that scans 35+ ML model formats for backdoors, blocks runtime prompt injection, and tracks agentic AI behavior. SOC 2 Type II certified.
- Microsoft's: Microsoft, founded 1975, is a public company (NASDAQ: MSFT) and the Redmond maker of Windows, Azure, GitHub and the Copilot assistants, with $331.8B of fiscal 2026 revenue.
- Nvidia: Santa Clara chipmaker that supplies the GPUs, networking, CUDA software and open Nemotron models behind most large AI training and inference clusters.
- OpenAI: OpenAI builds ChatGPT, the GPT-6 family (Astra, Sol, Luna), Codex and the OpenAI API. It reports 1.2B weekly ChatGPT users and an $852B valuation after its March 2026 round.
- OpenAI's Codex: Clones a GitHub repo into a sandbox, writes and tests code, then opens a pull request; OpenAI reported 20 million active users in August 2026.
- Openlayer: AI governance platform with an AI system inventory, 175+ evaluation tests and runtime guardrails that produce audit-ready evidence for regulators.
- Resemble AI: Generative voice AI and deepfake detection for enterprise trust
- Vega: Vega is Nebula Security's AI agent that has found 730+ real bugs, including 3 Chrome V8 RCEs, and now scans codebases via GitHub App, CLI, or MCP.
Sources
Still deciding?
This guide covers a handful of options. Smart Match checks every listing in the directory against how you actually work and what you can spend, then hands you the shortlist and the reason behind each pick.
Find your toolsRelated guides
- AI Development Services in 2026: Which Layer You Actually NeedBuyer's guideHow to pick, across a category
- The AI Tool Ecosystem in 2026: Buy the Meter, Not the CategoryBuyer's guideHow to pick, across a category
- AMD Buys World Labs for $8.2B: What It Means for Marble UsersAnalysisWhat changed and who it affects
- Archal vs ReasonBlocks: You're Not Choosing Between Them, You're Choosing WhenComparisonHead-to-head, with a verdict
- Attio vs HubSpot in 2026: Which CRM for a Startup?ComparisonHead-to-head, with a verdict
- Best Agentic AI in 2026: Manus, Genspark and the Platforms That Finish Whole TasksBuyer's guideHow to pick, across a category